Privacy & Policy
Privacy Badger anti-tracking tool lands on macOS Safari 26.5+ for 4M+ users
The Electronic Frontier Foundation has released its free tracker-blocking extension for Safari on macOS, requiring version 26.5 or higher to install.
Privacy & Policy coverage from Vector Bulletin holds 18 articles, 15 of them reference guides. The newest was published on October 20, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include NIST Privacy Framework and FTC: Privacy and Security.
The Electronic Frontier Foundation has released its free tracker-blocking extension for Safari on macOS, requiring version 26.5 or higher to install.
Credential reuse across unrelated platforms turns a minor external data leak into an immediate internal network compromise for small teams.
Small organisations hold more sensitive records than they realise, creating legal exposure without proportional business value.
Researchers find Discover-Tech used certified ad platforms to infect mobile devices without user interaction.
The ICO issued an enforcement notice after officers used a retail crime platform unlawfully, uploading details of 179 people without required safeguards.
Deleted records rarely vanish instantly due to system architecture, so containment of the initial leak matters more than chasing copies across the web.
Biometric templates are immutable secrets that cannot be reset when compromised, creating a permanent liability for identity verification systems.
Most organisations fail these requests not because of legal complexity, but because they cannot locate the data across fragmented legacy systems and shadow IT.
Privacy focused browsers reduce tracking but often break site functionality, forcing a trade-off between anonymity and usability that most users never configure correctly.
Most organisations fail CCPA compliance not because of missing policies, but because they cannot prove they have deleted data across all connected systems.
Encrypted DNS traffic hides your query content from intermediaries but reveals the resolver IP address to your network operator.
Using HTTP for simple requests can reduce server load, but mixing protocols exposes session tokens to interception by network-level adversaries.
Opting out triggers a manual review process that often fails to stop re-aggregation from public records and passive collection channels.
Encryption keys never touch the server, meaning the provider cannot read your messages even if compelled to do so by law.
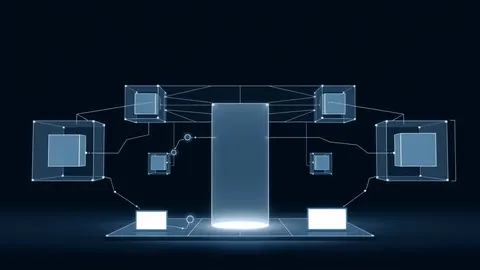
Embedding privacy controls into system architecture reduces liability more effectively than retroactive policy updates or user consent forms.
Email aliases route messages to a single inbox by rewriting headers, offering convenience but exposing your primary identity to determined adversaries.
File metadata often contains more operational detail than the document content, exposing device identifiers and editing histories that standard privacy tools miss.
Move beyond compliance checklists to understand how privacy audits map data flows, identify blind spots and reduce residual risk across your infrastructure.