Privacy & Policy
Personal data for small businesses: how to collect less and survive
Small organisations hold more sensitive records than they realise, creating legal exposure without proportional business value.
Everything Vector Bulletin has reported about data privacy: 12 stories, newest first. Part of our Privacy & Policy coverage.
Small organisations hold more sensitive records than they realise, creating legal exposure without proportional business value.
The ICO issued an enforcement notice after officers used a retail crime platform unlawfully, uploading details of 179 people without required safeguards.
Biometric templates are immutable secrets that cannot be reset when compromised, creating a permanent liability for identity verification systems.
Most organisations fail these requests not because of legal complexity, but because they cannot locate the data across fragmented legacy systems and shadow IT.
Most organisations fail CCPA compliance not because of missing policies, but because they cannot prove they have deleted data across all connected systems.
Removing data from search engines and social platforms does not erase it from broker databases or dark web repositories, requiring a layered removal strategy.
Using HTTP for simple requests can reduce server load, but mixing protocols exposes session tokens to interception by network-level adversaries.
Encryption keys never touch the server, meaning the provider cannot read your messages even if compelled to do so by law.
Most teams assume output filtering prevents leaks, but the real exposure occurs when context windows ingest unredacted source material before processing begins.
Most security teams overestimate the value of isolated data points while underestimating the danger of non-sensitive metadata when combined with other sources.
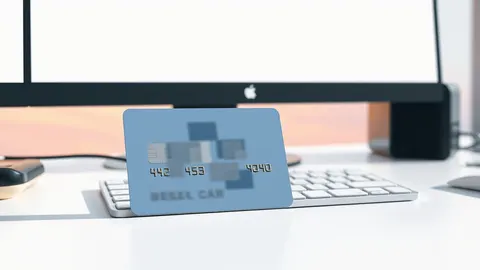
Data masking creates a usable but non-functional replica of production data, allowing development teams to test software without risking exposure of real customer records.
Notification deadlines often start the moment you detect the breach, not when you confirm data was stolen, forcing teams to act on incomplete evidence.