Vulnerabilities coverage from Vector Bulletin holds 50 articles, 20 of them reference guides. The newest was published on October 17, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include CVE Program and OWASP Top Ten.
Progress has released updates for its managed file transfer platform to address twelve vulnerabilities, including critical flaws that enable authentication bypass and privilege escalation.
Misconfigurations in certificate validation and session handling often bypass vendor patches, leaving infrastructure exposed to lateral movement attacks.
Runtime application self-protection inspects data at the point of use within the process, bypassing the signature limitations that often blind external network defences.
Physical memory cell interference allows remote attackers to bypass software security controls, exposing small organisations to data theft without network intrusion.
Standard address space layout randomisation fails against heap overflows because attackers exploit predictable metadata structures within the heap itself rather than targeting static addresses.
Publicly accessible .git folders allow attackers to reconstruct your entire source code history, including credentials and deployment scripts that were never meant for public consumption.
Sandbox escapes rely on the assumption that untrusted code cannot influence the host kernel, a premise that breaks when memory management flaws allow boundary traversal.
Most privilege escalation attempts fail because attackers overlook legacy services and misconfigured file permissions rather than exploiting complex kernel flaws.
Processors execute instructions ahead of time to gain speed, leaving temporary data traces that attackers can measure to reconstruct sensitive information.
A critical flaw in the Mang Board WordPress plugin allows attackers to inject malicious SQL commands, risking significant data exposure for site administrators.
A flaw in Dell’s Terraform tool ignores server identity, allowing attackers to intercept management traffic and steal credentials via man-in-the-middle attacks.
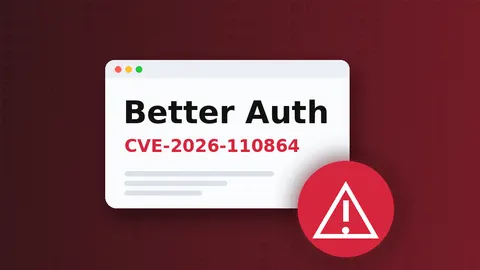
Unauthenticated attackers can hijack accounts in Better Auth versions before 1.7.7 by exploiting a flaw in the OAuth Proxy plugin that permits profile forgery.
A high-severity memory corruption bug in Microsoft Excel allows remote attackers to run arbitrary code on affected systems without prior authentication.
Microsoft has released patches for a high-severity denial-of-service vulnerability in .NET that allows remote attackers to crash services via uncontrolled recursion.
Microsoft has released updates for System.Security.Cryptography.Xml to fix a high-severity flaw that allows attackers to deny service via unbounded resource use.