Data Breaches
Implement Mobile Device Management: A Step-by-Step Rollout Guide
Separating corporate data from personal use requires containerisation, which enforces policy without exposing private messages or photos to your security team.
Data Breaches coverage from Vector Bulletin holds 11 articles, 11 of them reference guides. The newest was published on October 14, 2026. New stories are added as soon as they are confirmed, from more than 150 sources checked as often as every 45 seconds. Each story lists its sources. Primary sources we follow for this section include FTC: Data Breach Response, A Guide for Business and Have I Been Pwned.
Separating corporate data from personal use requires containerisation, which enforces policy without exposing private messages or photos to your security team.
Auditors rarely test security controls directly; they verify the administrative trail that proves you tested them, shifting the burden of proof entirely.
Unencrypted backups often contain more sensitive data than live systems, yet they receive fewer security controls and less frequent monitoring.
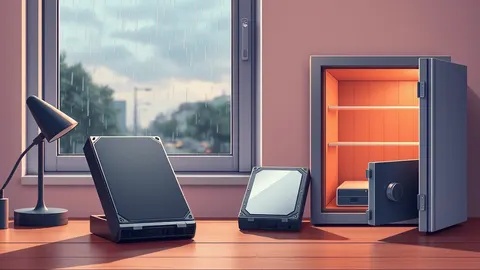
The 3-2-1 backup rule prevents data loss by enforcing geographical separation and media diversity, ensuring that a single point of failure cannot erase your entire history.
Synthetic identity fraud combines real and fake data to create persons who never existed, bypassing standard identity verification checks.
Passwords fail because they are static secrets that travel over networks, while device binding creates a persistent state that attackers cannot easily replicate.
Removing data from search engines and social platforms does not erase it from broker databases or dark web repositories, requiring a layered removal strategy.
Medical identity theft rarely involves stealing a physical card; it exploits the fragmented nature of health data to create synthetic profiles for service fraud.
Most security teams overestimate the value of isolated data points while underestimating the danger of non-sensitive metadata when combined with other sources.
Data masking creates a usable but non-functional replica of production data, allowing development teams to test software without risking exposure of real customer records.
Notification deadlines often start the moment you detect the breach, not when you confirm data was stolen, forcing teams to act on incomplete evidence.